← Back to all projects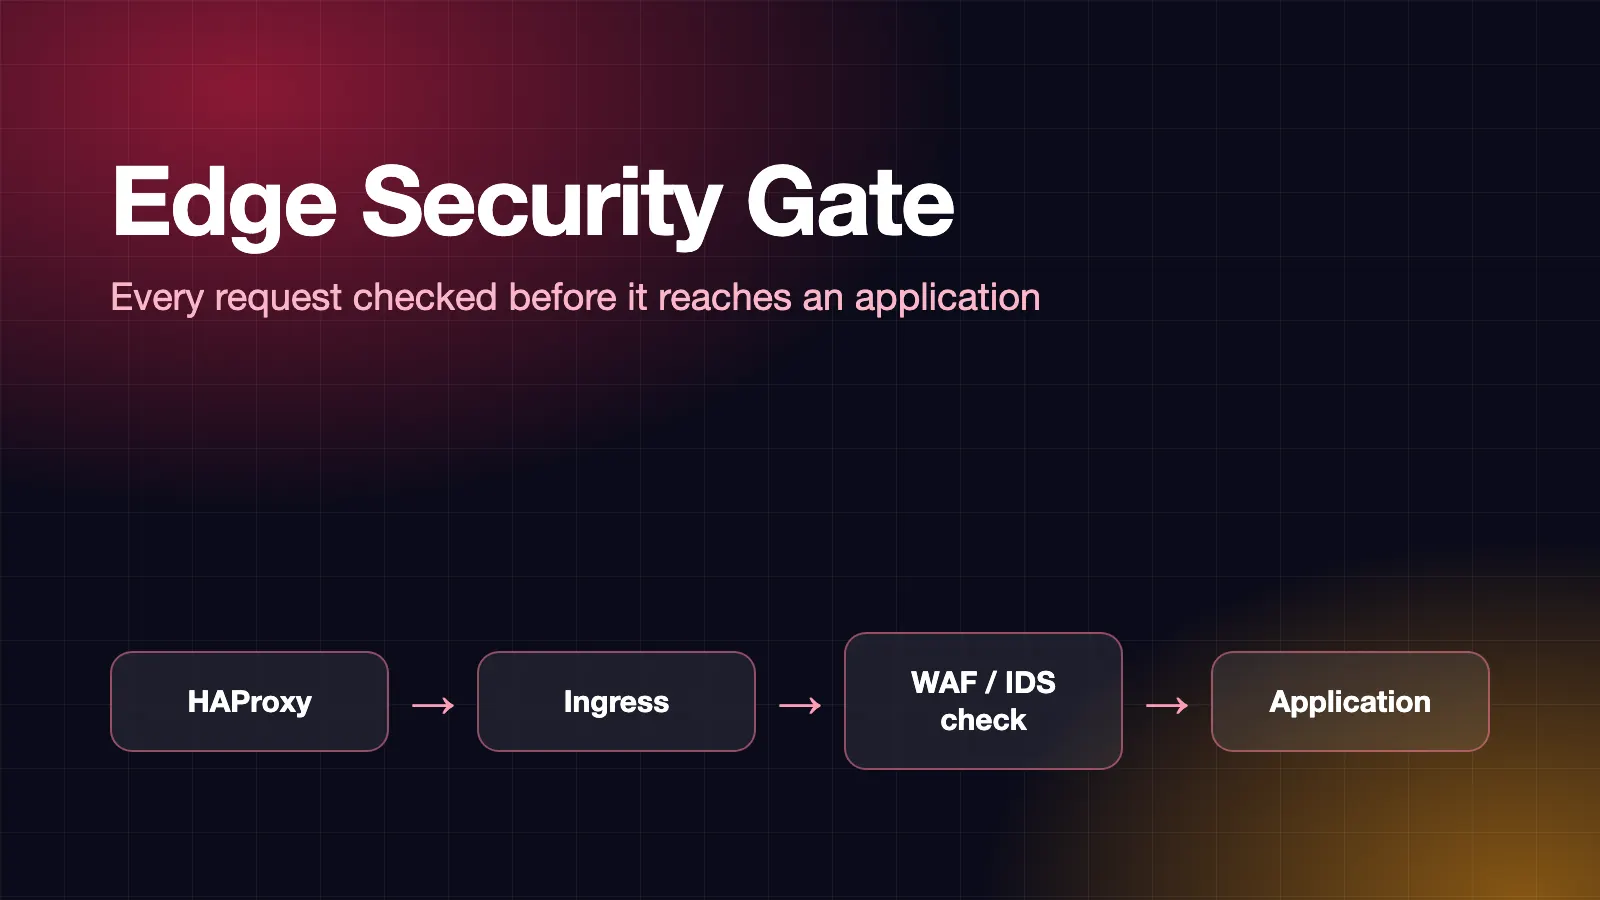
Edge Security Gate
Bot and attack protection at the edge of the Kubernetes platform: every request is checked before it reaches an application, with WAF and intrusion-detection rules, an opt-in bot challenge, and bans shared across the cluster and pushed out to the HAProxy front door. Run from its own control panel.
Technology
backendpython
devopskubernetestraefikhaproxydocker
toolswafids
Edge Security Gate
What I built
- Inline checks: a DaemonSet on every worker answers a forward-auth check for every request through the ingress, so bad traffic is stopped before it reaches any application.
- Detections: WAF and IDS signatures, with detections that ban.
- Bot gate: an opt-in challenge per site for automated traffic.
- Shared memory: an IP shield shared across the cluster, with bans exported to the HAProxy front door so repeat offenders are refused at the edge.
- Control panel: a console built as a module on the multi-tenant framework.
Private system: a walkthrough or live demo is available on request.